I wrote up what I found analysing a month of sample web logs in Splunk, including two wrong anomaly searches and why one busy IP wasn't an attacker. For people already running Grafana with Loki, what made you add a SIEM, or did you decide you didn't need one?
Who Did What, and Could You Prove It?
General Source:https://dev.to/adelusheriff/who-did-what-and-could-you-prove-it-4jkj
Who Did What, and Could You Prove It?
dev.to DevOps0 views
PreviousTerraform to OpenTofu Migration: A Complete Infrastructure as Code Planning GuideNextI have create a website (j'ai creer un site web)
Related posts

US voters roundly reject data centers in ballot measures
0Hacker News
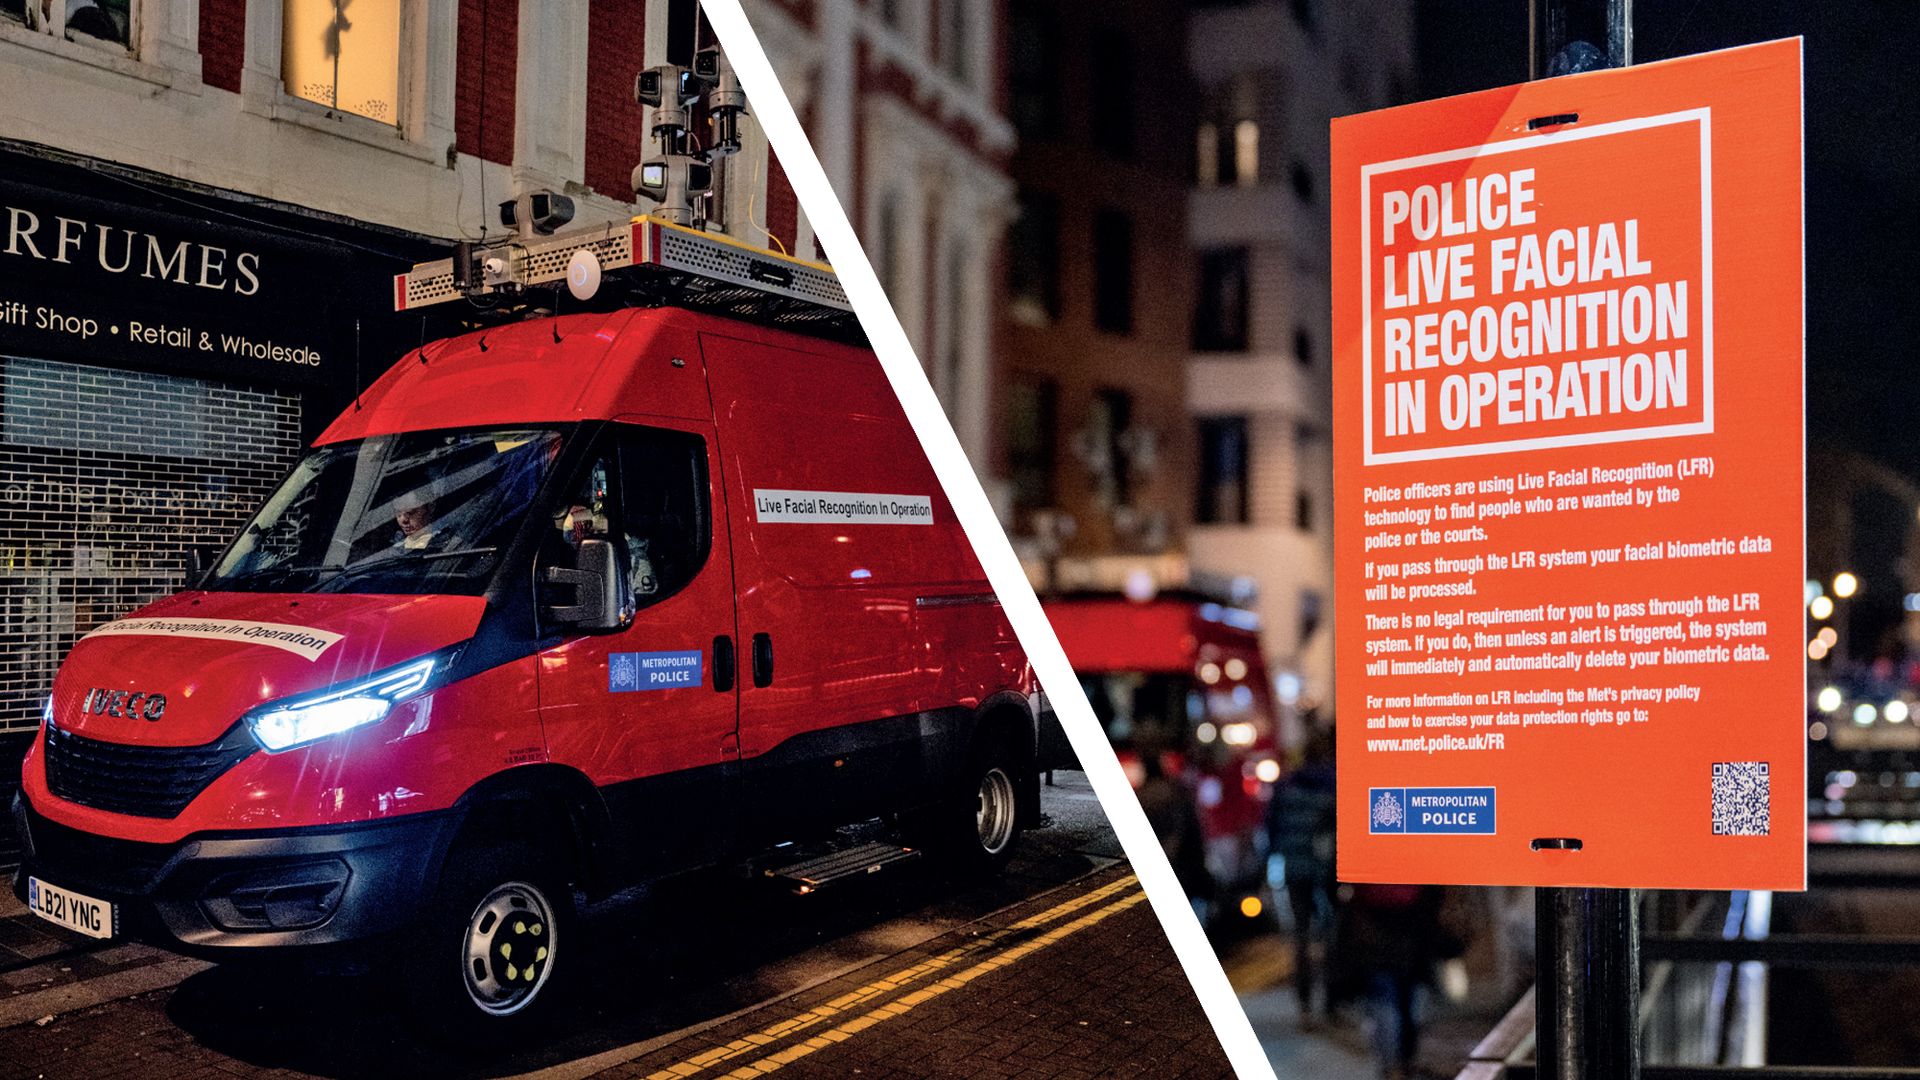
UK policing minister promises new facial recognition laws after criticisms
0TechRadar
How to watch College Basketball 2026/27: Free NCAA Live Streams & TV Channels
0TechRadar
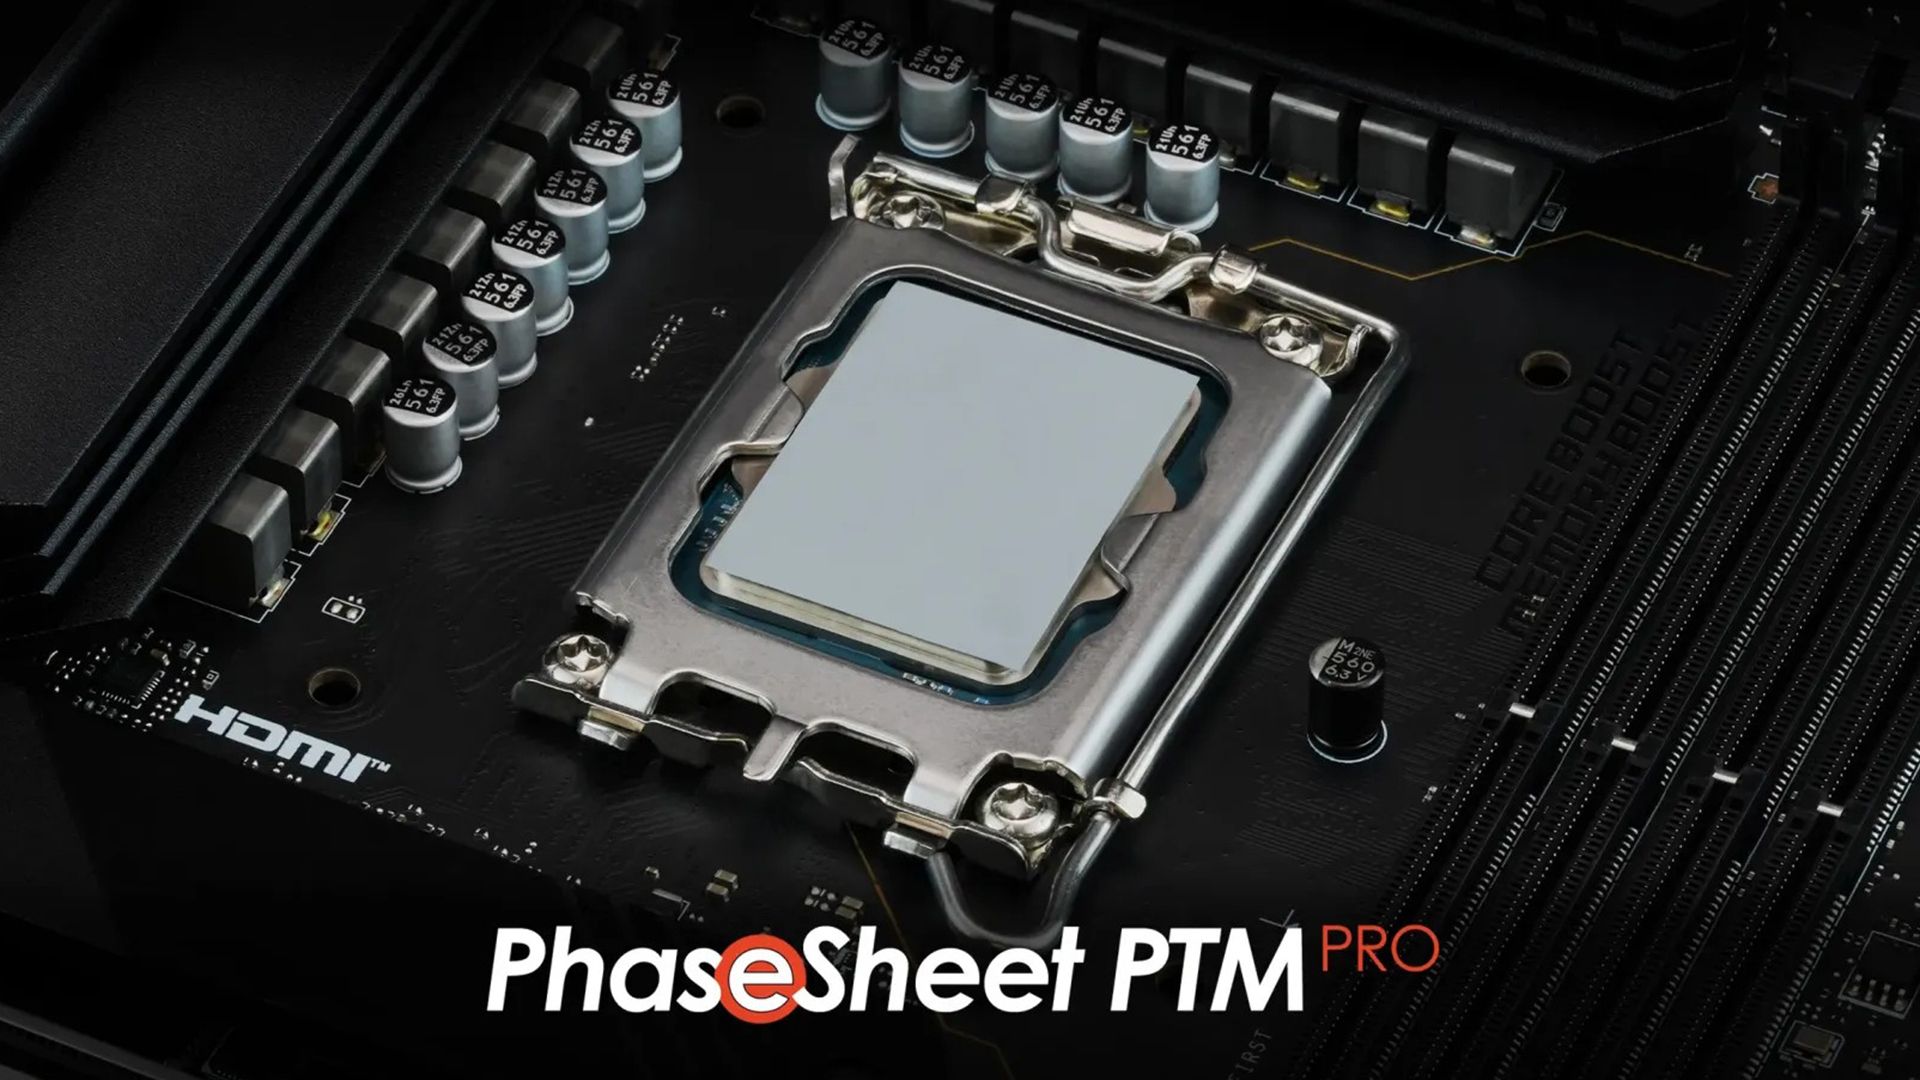
Thermal Grizzly launches PhaseSheet PTM Pro with improved thermal conductivity — new thermal pad promises easier installation and better cooling performance
0Tom's Hardware

A tiny squeeze dramatically changes the magnetism of exotic materials
0Science Daily Tech

MIT scientists break a 20-year rule and unlock never-before-seen crystal structures
0Science Daily Tech